One place for all your SBOMs
SBOM-HQ™ is your command center for managing software — whether you build it, buy it, or use it. Integrate, analyze, and respond to vulnerabilities faster than ever before.
SBOM-HQ™ gives software consumers end‑to‑end visibility and control of the supply chain. See how SBOM-HQ™ protects your software supply chain in action.
While most SBOM solutions stop at the software development lifecycle, SBOM-HQ™ goes further. It empowers software consumers to continuously monitor not only what they build, but also what they buy, from design and procurement, through integration, all the way to production in their own data centers. With SBOM-HQ™, transparency extends beyond development, delivering full visibility and control across the entire software supply chain.
SBOM-HQ™ is an ideal solution for managing the entire software supply chain ecosystem. It helps any size organization meet ongoing compliance requirements for mandates such as the Cyber Resilience Act (CRA), the Digital Operations Resilience Act (DORA), the New York State Department of Financial Services 500 (DFS500), and other mandates from around the globe that require the use of Software Bills of Materials (SBOMs).
Ensure software quality
Every software component is enriched with real-time risk insights—so you know exactly what’s entering your environment.
Get real-time alerts
Stay ahead of threats—SBOM-HQ™ alerts you instantly to new vulnerabilities affecting your software.
Mitigate risks as they appear
Stay secure by fixing risks the moment they appear and safeguard every layer of your environment.
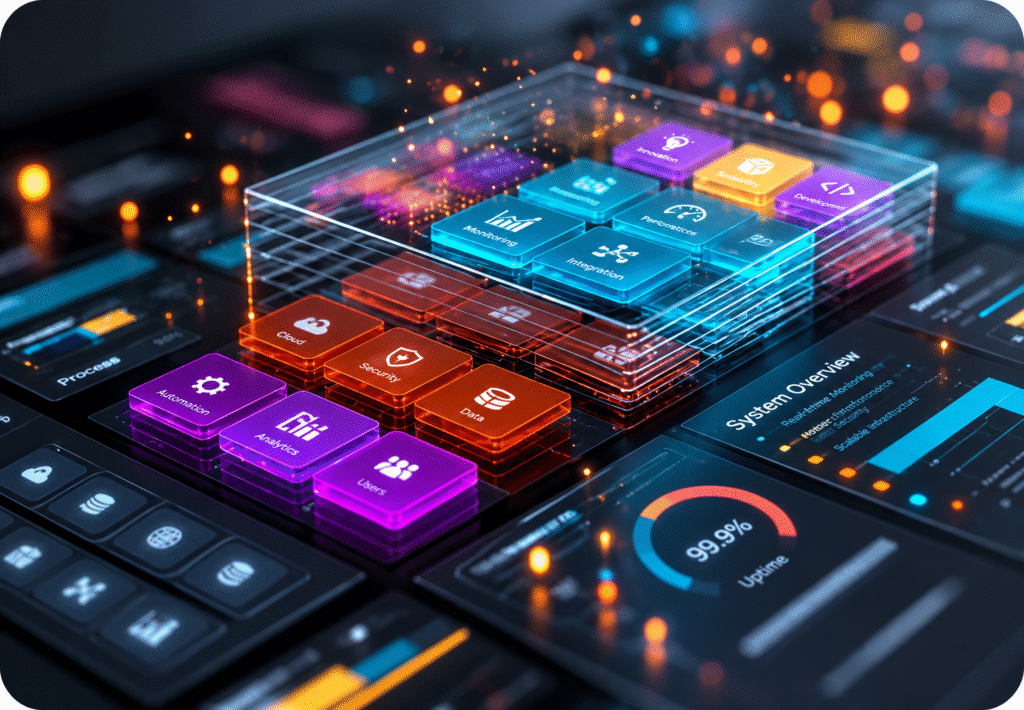
See how SBOM-HQ™ protects your software supply chain in action
Watch our quick walkthrough to learn how SBOM-HQ™ detects vulnerabilities, automates compliance, and gives your team full control over software components in real time!
Track vulnerabilities, prioritize risks, and take action with full visibility from source to endpoint
SBOM-HQ™ ingests your software bills of materials, analyzes components, detects vulnerabilities in real time, and tells you exactly where and how to act. All in one connected pipeline.
Upload SBOM
This step ensures the system has the necessary data about libraries, versions, and dependencies.
Analyze
Once the SBOM is uploaded, the system analyzes the components against known vulnerabilities and risks.
This process highlights weaknesses or outdated packages that may need attention.
Get Insights
After the analysis, the system provides clear insights about security, licensing, and compliance.
These insights help teams decide what actions to prioritize and how to improve their software posture
Monitor
Finally, the system continuously monitors the components for new vulnerabilities over time.
This ensures that teams are alerted quickly whenever a new issue is discovered in their dependencies.
Designed to support all teams engaged in the use and operation of software.
DevOps
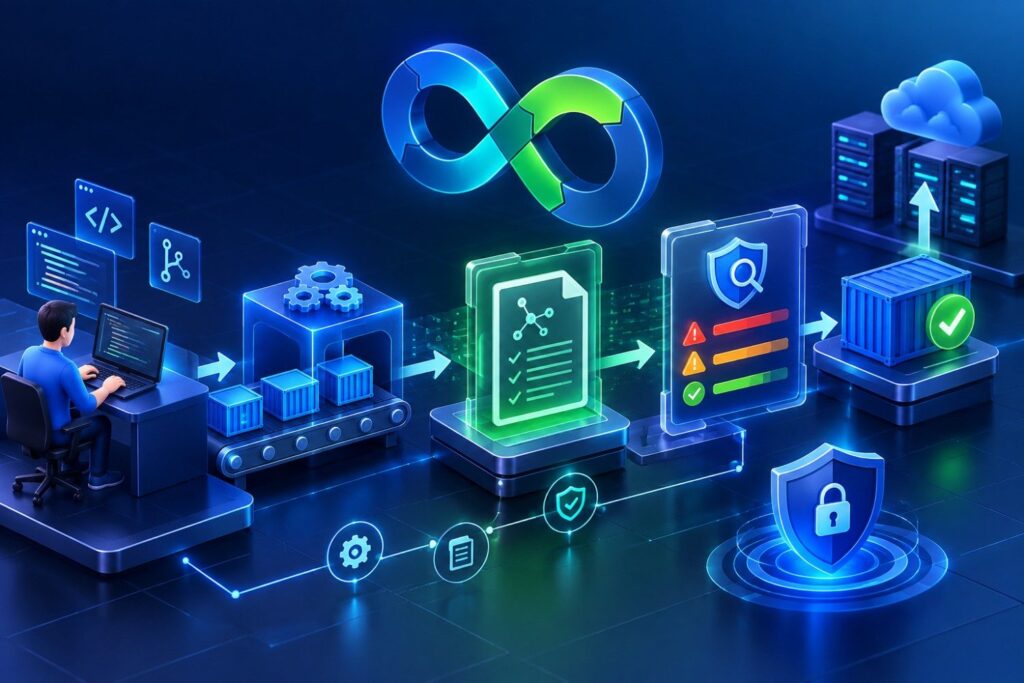
Integrates into CI/CD to generate and enrich SBOMs with real-time risk data, ensuring secure and compliant releases.
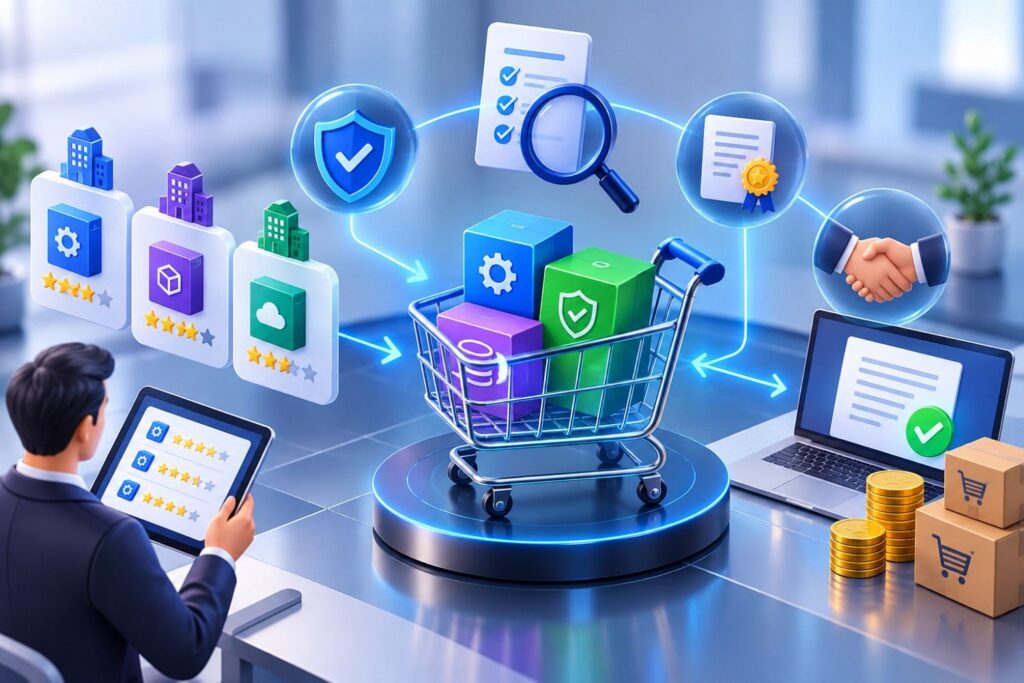
Procurement
Equips teams with insights into software quality and licensing risks, enabling smarter vendor selection & safer software purchases.
CyberSec Team
Evaluating cybersecurity aspects of the software purchased and monitoring new vulnerabilities that appear.
ITOps
Spots vulnerabilities the moment they appear. It safeguards your business with proactive risk control.
Legal & Licensing Teams
Delivers clear visibility into open-source licenses, flags conflicts early, and provides audit-ready compliance reports.

Reduce your costs and improve compliance
Get a free 30-minute strategy session with our Lead ITAM Consultant.

Eracent helps its customers meet the challenges of managing software licenses and computing assets in today’s complex and evolving IT environments.
Useful Links
Our Services
Contact Us
519 Easton Road, Riegelsville, PA 18077, USA
+1- 908-537-6520
Email Support
Copyright 2026, Eracent. All Rights Reserved.
